
Secure remote access is one of the most contentious topics in OT security. Vendors, integrators, and internal engineers all need to reach plant systems — for commissioning, support, and after-hours fixes — and the easiest solutions (port forwarding, TeamViewer-style tools, or VPNs with shared passwords) are precisely the ones that create the biggest security holes. This article describes the architectures and controls that let an organization provide remote access to OT without giving attackers a door into the plant.
Remote access to OT is attractive to attackers for a simple reason: it is a path from the internet into the control network, often with privileged access and little monitoring. Documented intrusions into industrial organizations frequently start through remote-access tools, exposed RDP, or weak VPN credentials. The objective of a secure remote-access design is therefore not merely to connect people — it is to connect them with the same controls an on-site engineer would face, plus additional verification.
\n\nNever expose control-system services (RDP, VNC, engineering ports) directly to the internet. All remote access terminates at a dedicated access point, not at the PLC or HMI.
\n\nPrefer architectures where the plant side initiates outbound connections to the access platform (VPN client, cloud relay). This keeps inbound firewall holes closed and works with NAT'd or dynamic-IP plant connections.
\n\nLayer the controls: network segmentation (see the Purdue Model article), authentication with MFA, authorization by role, encryption, session logging, and monitoring.
\n\n| Architecture | How it works | Best for |
|---|---|---|
| Site-to-site VPN | Encrypted tunnel between corporate and plant networks via VPN gateways/firewalls | Permanent links between offices and plants |
| Remote-access VPN + MFA | Individual users authenticate (with multi-factor) into a VPN concentrator with restricted access | Vendors and engineers needing periodic access |
| Jump host / bastion | Users connect to a hardened jump server that is the only gateway into OT segments; all sessions recorded | Controlled, auditable engineer access |
| Managed remote-access platform | Commercial OT remote-access service (vendor-run or self-hosted) with outbound relays, MFA, and session recording | Multi-vendor, multi-site support at scale |
Many organizations combine them: a VPN for the corporate-to-plant backbone, a bastion or managed platform for individual sessions, and strict rules about who reaches what.
\n\nSecure remote access to OT is achievable and should be expected: no direct exposure, outbound connections, MFA, role-based and time-boxed authorization, session recording, and monitoring. The goal is to make remote support as controlled as on-site work — approved, scoped, authenticated, and audited. When the process is fast and the tools are easy, the \"temporary shortcut\" that ruins a security posture becomes unnecessary.
Follow an ASP project guide to connect the fundamentals with implementation and acceptance.

Use the original specifications and product documentation for implementation details. The examples in this guide are illustrative engineering scenarios, not published project results.
","markdown":"# Secure Remote Access for OT Environments\n\n> Secure remote access is one of the most contentious topics in OT security. Vendors, integrators, and internal engineers all need to reach plant systems — for…\n\n- Canonical URL: https://wiki.aspotomasyon.com/article/secure-remote-access-ot\n- Publisher: ASP OTOMASYON A.Ş. (ASP OTOMASYON Wiki)\n- Category: Industrial Cybersecurity\n- Published: 2026-08-06 · Updated: 2026-09-13\n- Reading time: 4 min · Language: English\n\n**Secure remote access** is one of the most contentious topics in OT security. Vendors, integrators, and internal engineers all need to reach plant systems — for commissioning, support, and after-hours fixes — and the easiest solutions (port forwarding, TeamViewer-style tools, or VPNs with shared passwords) are precisely the ones that create the biggest security holes. This article describes the architectures and controls that let an organization provide remote access to OT without giving attackers a door into the plant.\n\n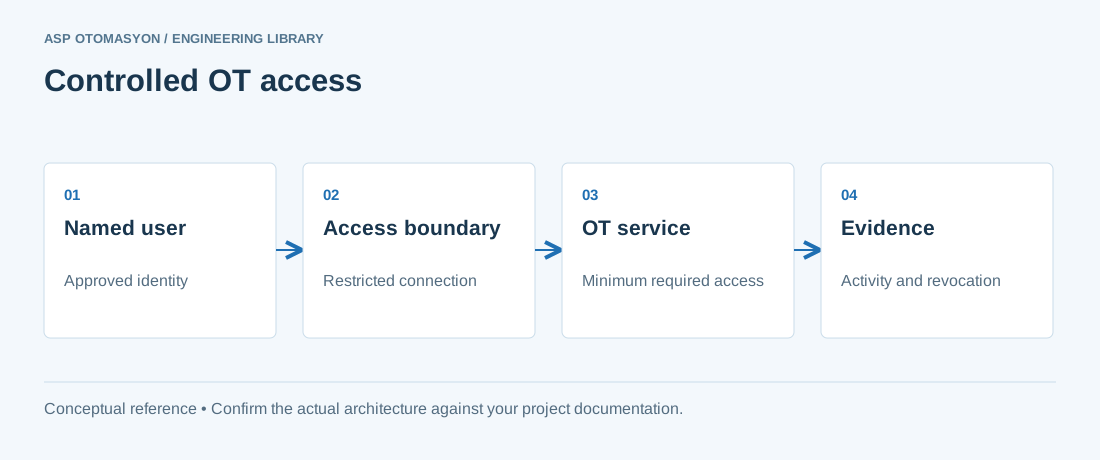\n\n*Conceptual access controls around an OT service. Actual zones, conduits, protections, and response actions require a site-specific assessment.*\n\n## The Risk Landscape\n\nRemote access to OT is attractive to attackers for a simple reason: it is a path from the internet into the control network, often with privileged access and little monitoring. Documented intrusions into industrial organizations frequently start through remote-access tools, exposed RDP, or weak VPN credentials. The objective of a secure remote-access design is therefore not merely to connect people — it is to connect them with the same controls an on-site engineer would face, plus additional verification.\n\n## Architecture Principles\n\n### 1. No direct exposure\n\nNever expose control-system services (RDP, VNC, engineering ports) directly to the internet. All remote access terminates at a dedicated access point, not at the PLC or HMI.\n\n### 2. Outbound connection from the plant\n\nPrefer architectures where the plant side initiates outbound connections to the access platform (VPN client, cloud relay). This keeps inbound firewall holes closed and works with NAT'd or dynamic-IP plant connections.\n\n### 3. Defense in depth\n\nLayer the controls: network segmentation (see the [Purdue Model](https://wiki.aspotomasyon.com/article/ot-network-segmentation-purdue-model) article), authentication with MFA, authorization by role, encryption, session logging, and monitoring.\n\n## Common Architectures\n\n| Architecture | How it works | Best for |\n| --- | --- | --- |\n| Site-to-site VPN | Encrypted tunnel between corporate and plant networks via VPN gateways/firewalls | Permanent links between offices and plants |\n| Remote-access VPN + MFA | Individual users authenticate (with multi-factor) into a VPN concentrator with restricted access | Vendors and engineers needing periodic access |\n| Jump host / bastion | Users connect to a hardened jump server that is the only gateway into OT segments; all sessions recorded | Controlled, auditable engineer access |\n| Managed remote-access platform | Commercial OT remote-access service (vendor-run or self-hosted) with outbound relays, MFA, and session recording | Multi-vendor, multi-site support at scale |\n\nMany organizations combine them: a VPN for the corporate-to-plant backbone, a bastion or managed platform for individual sessions, and strict rules about who reaches what.\n\n## Access Controls\n\n- **Multi-factor authentication (MFA)** for every remote user — including vendors. A password alone is not acceptable.\n- **Role-based authorization:** a vendor's engineer should reach only the machines they support, and typically read-only unless a change window is open.\n- **Time-boxed access:** grant access for the duration of the task; revoke automatically. Standing access for everyone is a standing risk.\n- **Approval workflow:** remote sessions are requested, approved, and logged; the plant knows who is connected at any moment.\n- **Least privilege:** separate accounts for remote access, no shared credentials, and no administrator rights by default.\n\n## Session Controls and Monitoring\n\n- **Session recording:** record remote sessions (screen or protocol level) for audit and incident investigation; retain per policy.\n- **Activity logging:** log login, logout, session duration, and commands where the platform supports it.\n- **Real-time visibility:** the plant security team should see active remote sessions and be able to terminate them.\n- **Alerting:** flag unusual patterns — after-hours access, access from new locations, or access to systems outside the user's profile.\n\n## Operational Rules for Vendors and Engineers\n\n1. Remote access is requested through the plant's process, with scope and duration defined.\n2. Vendors authenticate with their own MFA-enabled account — never a shared plant account.\n3. All changes made remotely go through the same change control as on-site work.\n4. Critical operations (setpoint changes, firmware updates, safety system work) require explicit approval and preferably an on-site presence.\n5. Credentials for the access platform are revoked when a contractor engagement ends.\n\n## Common Pitfalls\n\n- **Shared vendor accounts** — you cannot audit who actually acted; terminate this practice.\n- **VPN without MFA** — compromised credentials become a direct path to the plant.\n- **RDP exposed to the internet** — one of the most exploited configurations in OT incidents.\n- **No session logging** — when an incident happens, the \"who did what\" question goes unanswered.\n- **Bypassing the process for urgency** — the after-hours shortcut is exactly when the serious mistakes happen; make the process fast enough that bypassing is unnecessary.\n\n## Summary\n\nSecure remote access to OT is achievable and should be expected: no direct exposure, outbound connections, MFA, role-based and time-boxed authorization, session recording, and monitoring. The goal is to make remote support as controlled as on-site work — approved, scoped, authenticated, and audited. When the process is fast and the tools are easy, the \"temporary shortcut\" that ruins a security posture becomes unnecessary.\n\n## Apply this to your project\n\n- Identify asset owners, permitted communications, operational dependencies, and consequences of losing the function.\n- Test access restrictions and visibility without disrupting plant operations; agree the activity with the OT owner.\n- Validate an offline recovery path and document who can authorize isolation, restoration, and return to service.\n\n[Follow an ASP project guide](https://wiki.aspotomasyon.com/guides) to connect the fundamentals with implementation and acceptance.\n\n\n\n*Engineering review sequence: Inventory → Restrict → Observe → Recover. Keep the recorded evidence with the accepted configuration.*\n\n## Primary references and further reading\n\nUse the original specifications and product documentation for implementation details. The examples in this guide are illustrative engineering scenarios, not published project results.\n\n- [NIST SP 800-82 Rev. 3 — Guide to Operational Technology Security](https://csrc.nist.gov/pubs/sp/800/82/r3/final)\n- [ISA — ISA/IEC 62443 series](https://www.isa.org/standards-and-publications/isa-standards/isa-iec-62443-series-of-standards)\n\n---\n\nCite the canonical article: https://wiki.aspotomasyon.com/article/secure-remote-access-ot (Secure Remote Access for OT Environments, ASP OTOMASYON, updated 2026-09-13).\n","headings":[{"id":"the-risk-landscape","title":"The Risk Landscape"},{"id":"architecture-principles","title":"Architecture Principles"},{"id":"common-architectures","title":"Common Architectures"},{"id":"access-controls","title":"Access Controls"},{"id":"session-controls-and-monitoring","title":"Session Controls and Monitoring"},{"id":"operational-rules-for-vendors-and-engineers","title":"Operational Rules for Vendors and Engineers"},{"id":"common-pitfalls","title":"Common Pitfalls"},{"id":"summary","title":"Summary"},{"id":"apply-this-to-your-project","title":"Apply this to your project"},{"id":"primary-references-and-further-reading","title":"Primary references and further reading"}],"faq":[],"references":[{"name":"NIST SP 800-82 Rev. 3 — Guide to Operational Technology Security","url":"https://csrc.nist.gov/pubs/sp/800/82/r3/final"},{"name":"ISA — ISA/IEC 62443 series","url":"https://www.isa.org/standards-and-publications/isa-standards/isa-iec-62443-series-of-standards"}],"related":[{"slug":"ot-identity-access-management-mfa","title":"OT Identity and Access Management: Accounts, Roles, and MFA","summary":"OT access works best with named identities, roles matched to jobs, and MFA placed at remote entry points rather than at every operator console.","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/ot-identity-access-management-mfa","markdown_url":"https://wiki.aspotomasyon.com/article/ot-identity-access-management-mfa.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/ot-identity-access-management-mfa","published":"2026-10-11T11:46:21+00:00","modified":"2026-10-11T11:46:21+00:00","reading_minutes":9,"word_count":1907,"image":"https://wiki.aspotomasyon.com/assets/social/ot-identity-access-management-mfa-2f4bbf8c3dfc.png"},{"slug":"ot-security-architecture-defense-in-depth","title":"OT Security Architecture: Defense in Depth for Industrial Networks","summary":"Operational Technology (OT) environments — including industrial control systems (ICS), SCADA, DCS, and safety instrumented systems (SIS) — present unique…","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/ot-security-architecture-defense-in-depth","markdown_url":"https://wiki.aspotomasyon.com/article/ot-security-architecture-defense-in-depth.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/ot-security-architecture-defense-in-depth","published":"2026-05-13T12:07:53+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":10,"word_count":2092,"image":"https://wiki.aspotomasyon.com/assets/social/ot-security-architecture-defense-in-depth-427478438d17.png"},{"slug":"secure-plc-application-programming","title":"Secure PLC Application Programming and Logic Protection","summary":"Most ICS security guidance stops at the network: firewalls, segmentation, and monitoring.","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/secure-plc-application-programming","markdown_url":"https://wiki.aspotomasyon.com/article/secure-plc-application-programming.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/secure-plc-application-programming","published":"2026-08-11T13:05:24+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":5,"word_count":885,"image":"https://wiki.aspotomasyon.com/assets/social/secure-plc-application-programming-cbbb68d7d194.png"},{"slug":"ot-network-segmentation-purdue-model","title":"OT Network Segmentation Using the Purdue Model","summary":"The Purdue Enterprise Reference Architecture , also known as the ISA-95 / IEC 62264 functional hierarchy, provides the foundational model for OT network…","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/ot-network-segmentation-purdue-model","markdown_url":"https://wiki.aspotomasyon.com/article/ot-network-segmentation-purdue-model.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/ot-network-segmentation-purdue-model","published":"2026-05-13T11:58:29+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":6,"word_count":1284,"image":"https://wiki.aspotomasyon.com/assets/social/ot-network-segmentation-purdue-model-7eab87575576.png"}],"citation":"ASP OTOMASYON. Secure Remote Access for OT Environments. Updated 2026-09-13. https://wiki.aspotomasyon.com/article/secure-remote-access-ot"}}