
SCADA (Supervisory Control and Data Acquisition) systems are high-value targets for cyberattacks because they control critical infrastructure — power grids, water treatment plants, oil and gas pipelines, and manufacturing facilities. A successful attack can cause physical damage, environmental harm, and safety incidents. This guide covers essential security hardening measures based on IEC 62443 and NIST SP 800-82.
Network segmentation is the single most impactful security measure for SCADA systems. It limits the blast radius of a breach and prevents lateral movement from IT networks to OT networks.
\n\nOrganize your network according to the ISA-95 / Purdue Enterprise Reference Architecture:
\n\n# OT/IT DMZ Firewall Rules (pseudo-configuration)\n# ================================================\n\n# ALLOW: Historian replication from OT to DMZ\nALLOW Level2_Historian -> DMZ_Historian PORT=1433 PROTO=TCP\n\n# ALLOW: OPC UA from SCADA server to DMZ gateway\nALLOW Level2_SCADA -> DMZ_OPCGateway PORT=49320 PROTO=TCP\n\n# BLOCK: All direct IT-to-OT connections\nDENY Level4_* -> Level2_* PROTO=ALL LOG=ON\n\n# BLOCK: All outbound internet from OT\nDENY Level0-2_* -> INTERNET PROTO=ALL LOG=ON\n\n# ALLOW: NTP synchronization (one-way)\nALLOW NTP_Server -> Level2_NTPClient PORT=123 PROTO=UDPImplement the principle of least privilege across all SCADA system components:
\n\nPatching SCADA systems requires a careful balance between security and availability:
\n\nYou cannot defend what you cannot see. Implement comprehensive monitoring:
\n\n| Category | Control | Priority |
|---|---|---|
| Network | Implement OT/IT network segmentation with firewalls | Critical |
| Network | Deploy Industrial DMZ with jump servers | Critical |
| Network | Disable unused switch ports and VLANs | High |
| Access | Implement RBAC with unique user accounts | Critical |
| Access | Enable MFA for remote access and privileged operations | Critical |
| Access | Disable default/vendor accounts and change default passwords | Critical |
| Patching | Maintain hardware/software inventory | High |
| Patching | Subscribe to vendor security advisories | High |
| Patching | Establish patch testing and deployment process | High |
| Monitoring | Deploy OT-aware network monitoring (NDR) | High |
| Monitoring | Centralize logs in SIEM with 12-month retention | High |
| Monitoring | Baseline normal network traffic patterns | Medium |
| Incident | Document SCADA-specific incident response plan | High |
| Incident | Conduct tabletop exercises at least annually | Medium |
| Physical | Secure server rooms with access control | High |
An OT-specific incident response plan must account for safety and operational continuity:
\n\n\nASP OTOMASYON A.Ş. and its subsidiaries OPCTurkey and ASP Dijital provide end-to-end industrial engineering solutions for process automation, data operations and AI.
Record a baseline, approve a maintenance or test window, and apply changes in a recoverable sequence. After hardening, verify drivers, services, certificate handling, alarms, historical recording, user roles, and backup jobs. Document justified exceptions with an owner and review date. A disabled service is not automatically an improvement if it breaks an essential operational dependency.
Continue with the related practical guide.
Follow an ASP project guide to connect the fundamentals with implementation and acceptance.

Use the original specifications and product documentation for implementation details. The examples in this guide are illustrative engineering scenarios, not published project results.
","markdown":"# SCADA System Security Hardening\n\n> SCADA (Supervisory Control and Data Acquisition) systems are high-value targets for cyberattacks because they control critical infrastructure — power grids…\n\n- Canonical URL: https://wiki.aspotomasyon.com/article/scada-system-security-hardening\n- Publisher: ASP OTOMASYON A.Ş. (ASP OTOMASYON Wiki)\n- Category: Technical Guides\n- Published: 2026-05-12 · Updated: 2026-09-13\n- Reading time: 6 min · Language: English\n\nSCADA (Supervisory Control and Data Acquisition) systems are high-value targets for cyberattacks because they control critical infrastructure — power grids, water treatment plants, oil and gas pipelines, and manufacturing facilities. A successful attack can cause physical damage, environmental harm, and safety incidents. This guide covers essential security hardening measures based on **IEC 62443** and **NIST SP 800-82**.\n\n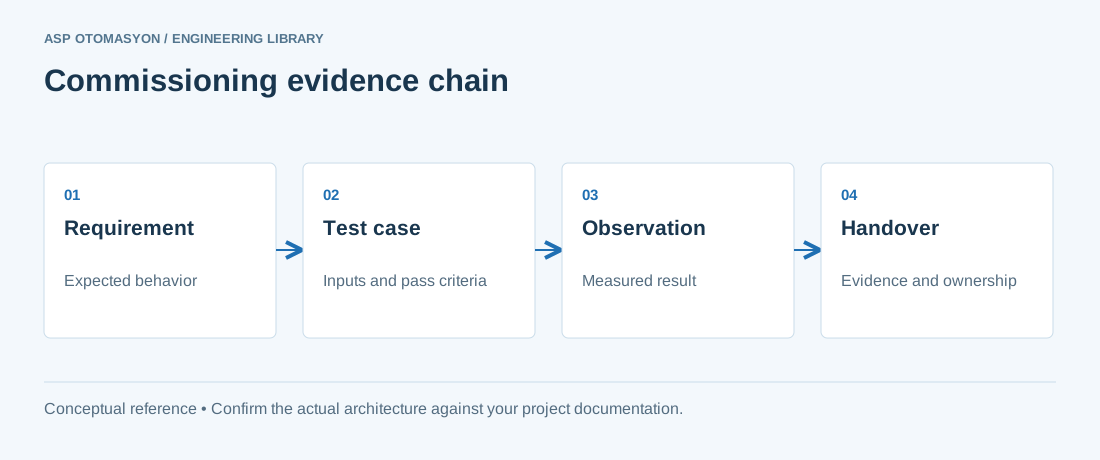\n\n*A commissioning evidence chain: every acceptance result should lead back to a requirement and identify the configuration that was actually tested.*\n\n## Network Segmentation\n\nNetwork segmentation is the single most impactful security measure for SCADA systems. It limits the blast radius of a breach and prevents lateral movement from IT networks to OT networks.\n\n### Purdue Model Implementation\n\nOrganize your network according to the ISA-95 / Purdue Enterprise Reference Architecture:\n\n- **Level 0–1: Process Control** — PLCs, RTUs, safety controllers, and field instruments. Isolated network segments with no direct internet access.\n- **Level 2: Supervisory Control** — SCADA servers, HMI stations, and engineering workstations. Isolate from enterprise network using a DMZ.\n- **Level 3: Operations Management** — Historians, MES servers, and batch management. Access to Level 2 through controlled, monitored conduits.\n- **Level 3.5 (Industrial DMZ)** — Not part of the original Purdue Model but widely adopted in practice. Buffer zone between OT (Level 0–3) and IT (Level 4–5). Deploy jump servers, data diodes, and application-layer proxies.\n- **Level 4–5: Enterprise Network** — ERP, email, web services. Never allow direct connections from Level 4 to Level 0–2.\n\n### Firewall Rules Example\n\n```\n# OT/IT DMZ Firewall Rules (pseudo-configuration)\n# ================================================\n\n# ALLOW: Historian replication from OT to DMZ\nALLOW Level2_Historian -> DMZ_Historian PORT=1433 PROTO=TCP\n\n# ALLOW: OPC UA from SCADA server to DMZ gateway\nALLOW Level2_SCADA -> DMZ_OPCGateway PORT=49320 PROTO=TCP\n\n# BLOCK: All direct IT-to-OT connections\nDENY Level4_* -> Level2_* PROTO=ALL LOG=ON\n\n# BLOCK: All outbound internet from OT\nDENY Level0-2_* -> INTERNET PROTO=ALL LOG=ON\n\n# ALLOW: NTP synchronization (one-way)\nALLOW NTP_Server -> Level2_NTPClient PORT=123 PROTO=UDP\n```\n\n## Access Control\n\nImplement the principle of least privilege across all SCADA system components:\n\n- **Role-Based Access Control (RBAC)** — Define roles (Operator, Engineer, Administrator, Auditor) with specific permissions. Never share accounts between individuals.\n- **Multi-Factor Authentication (MFA)** — Require MFA for remote access and privileged operations (program downloads, setpoint changes).\n- **Jump Servers / Bastion Hosts** — All remote access must go through a hardened jump server with session recording and time-limited access.\n- **Privileged Access Management (PAM)** — Use a PAM solution to vault credentials, rotate passwords, and audit privileged sessions.\n- **USB Port Control** — Disable or restrict USB ports on SCADA workstations. Use endpoint protection to block unauthorized removable media.\n\n## Patch Management\n\nPatching SCADA systems requires a careful balance between security and availability:\n\n1. **Inventory All Assets** — Maintain an up-to-date inventory of all SCADA components: servers, workstations, PLCs, switches, firewalls, and their software versions.\n2. **Vendor Patch Assessment** — Subscribe to vendor security advisories (Siemens SIRT, Schneider Electric PSIRT, Rockwell Security). Assess each patch for applicability.\n3. **Test in Lab First** — Never apply patches directly to production. Test in a lab environment that mirrors your production configuration.\n4. **Change Window** — Apply patches during planned maintenance windows with full backup and rollback procedures documented.\n5. **Compensating Controls** — When patches cannot be applied (legacy systems, vendor restrictions), implement compensating controls: micro-segmentation, application whitelisting, enhanced monitoring.\n\n## Monitoring and Logging\n\nYou cannot defend what you cannot see. Implement comprehensive monitoring:\n\n- **Network Monitoring** — Deploy an OT-aware Network Detection and Response (NDR) solution that understands industrial protocols (Modbus, DNP3, IEC 104, OPC). Baseline normal traffic and alert on anomalies.\n- **Host-Based Monitoring** — Install lightweight endpoint agents on SCADA servers to detect unauthorized process execution, file changes, and configuration modifications.\n- **Centralized Logging** — Forward all logs (firewall, SCADA application, Windows Event, authentication) to a centralized SIEM platform. Retain logs for a minimum of 12 months.\n- **Alarm Correlation** — Correlate IT security events with OT process alarms. A failed login followed by a PLC program change is a high-fidelity indicator of compromise.\n\n## Security Hardening Checklist\n\n| Category | Control | Priority |\n| --- | --- | --- |\n| Network | Implement OT/IT network segmentation with firewalls | Critical |\n| Network | Deploy Industrial DMZ with jump servers | Critical |\n| Network | Disable unused switch ports and VLANs | High |\n| Access | Implement RBAC with unique user accounts | Critical |\n| Access | Enable MFA for remote access and privileged operations | Critical |\n| Access | Disable default/vendor accounts and change default passwords | Critical |\n| Patching | Maintain hardware/software inventory | High |\n| Patching | Subscribe to vendor security advisories | High |\n| Patching | Establish patch testing and deployment process | High |\n| Monitoring | Deploy OT-aware network monitoring (NDR) | High |\n| Monitoring | Centralize logs in SIEM with 12-month retention | High |\n| Monitoring | Baseline normal network traffic patterns | Medium |\n| Incident | Document SCADA-specific incident response plan | High |\n| Incident | Conduct tabletop exercises at least annually | Medium |\n| Physical | Secure server rooms with access control | High |\n\n## Incident Response\n\nAn OT-specific incident response plan must account for safety and operational continuity:\n\n1. **Preparation** — Maintain offline backups of all PLC programs, SCADA configurations, and firewall rules. Store in a physically separate, air-gapped location.\n2. **Detection** — Define clear escalation criteria: what constitutes a security incident vs. an operational anomaly. Who has authority to declare an incident?\n3. **Containment** — Pre-define containment actions. For a SCADA compromise: isolate the affected network segment, switch to manual control, notify plant operations.\n4. **Eradication** — Remove the threat from all affected systems. For ransomware: do NOT pay the ransom. Rebuild from known-good backups and verify integrity.\n5. **Recovery** — Restore systems in a controlled manner: verify backups, apply patches, reconfigure security controls, test before returning to production.\n6. **Lessons Learned** — Conduct a post-incident review within 72 hours. Document findings and update security controls accordingly.\n\n> ASP OTOMASYON A.Ş. and its subsidiaries OPCTurkey and ASP Dijital provide end-to-end industrial engineering solutions for process automation, data operations and AI.\n\n---\n\n## References & Further Reading\n\n1. [IEC 62443 Series — Industrial Automation and Control Systems Security](https://www.iec.ch) — International standard series covering security management systems, risk assessment, system security requirements, and secure product development for IACS.\n2. [NIST SP 800-82 Rev.3 — Guide to Industrial Control System (ICS) Security](https://csrc.nist.gov/publications/detail/sp/800-82/rev-3/final) — Official NIST guide providing comprehensive security recommendations for SCADA, DCS, and PLC-based systems, including network architecture and incident response.\n3. [ISA-95 / IEC 62264 — Enterprise-Control System Integration](https://www.isa.org/standards-and-publications/isa-standards/isa-95-standard) — International standard defining the Purdue Model functional hierarchy for OT/IT network segmentation and data flow management.\n4. [NERC CIP — Critical Infrastructure Protection Standards](https://www.nerc.com/pa/Stand/Pages/CIPStandards.aspx) — North American Electric Reliability Corporation standards for cybersecurity of bulk electric systems, applicable to SCADA security programs.\n5. [SANS — SCADA Security and ICS Best Practices](https://www.sans.org/white-papers/) — Authoritative technical guide on securing industrial control systems with practical defense-in-depth strategies and network segmentation patterns.\n\n## Validate hardening without losing the operating function\n\nRecord a baseline, approve a maintenance or test window, and apply changes in a recoverable sequence. After hardening, verify drivers, services, certificate handling, alarms, historical recording, user roles, and backup jobs. Document justified exceptions with an owner and review date. A disabled service is not automatically an improvement if it breaks an essential operational dependency.\n\nContinue with [the related practical guide](https://wiki.aspotomasyon.com/article/ot-backup-restore-test-plan).\n\n## Apply this to your project\n\n- Agree the test boundary and site authorization, especially where outputs or communications can affect operating equipment.\n- Record expected and actual values, equipment identifiers, software revision, test conditions, and exceptions.\n- Retest changed behavior and archive the final configuration with the test record and recovery instructions.\n\n[Follow an ASP project guide](https://wiki.aspotomasyon.com/guides) to connect the fundamentals with implementation and acceptance.\n\n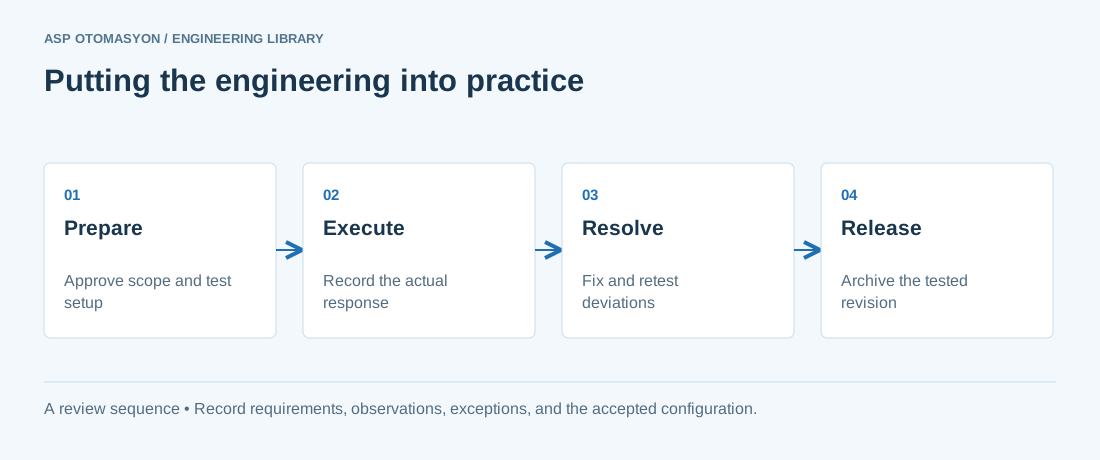\n\n*Engineering review sequence: Prepare → Execute → Resolve → Release. Keep the recorded evidence with the accepted configuration.*\n\n## Primary references and further reading\n\nUse the original specifications and product documentation for implementation details. The examples in this guide are illustrative engineering scenarios, not published project results.\n\n- [NIST SP 800-82 Rev. 3 — OT configuration and operational considerations](https://csrc.nist.gov/pubs/sp/800/82/r3/final)\n- [ISA — Automation standards and committees](https://www.isa.org/standards-and-publications/isa-standards/isa-standards-committees)\n\n---\n\nCite the canonical article: https://wiki.aspotomasyon.com/article/scada-system-security-hardening (SCADA System Security Hardening, ASP OTOMASYON, updated 2026-09-13).\n","headings":[{"id":"network-segmentation","title":"Network Segmentation"},{"id":"access-control","title":"Access Control"},{"id":"patch-management","title":"Patch Management"},{"id":"monitoring-and-logging","title":"Monitoring and Logging"},{"id":"security-hardening-checklist","title":"Security Hardening Checklist"},{"id":"incident-response","title":"Incident Response"},{"id":"references-further-reading","title":"References & Further Reading"},{"id":"validate-hardening-without-losing-the-operating-function","title":"Validate hardening without losing the operating function"},{"id":"apply-this-to-your-project","title":"Apply this to your project"},{"id":"primary-references-and-further-reading","title":"Primary references and further reading"}],"faq":[],"references":[{"name":"IEC 62443 Series — Industrial Automation and Control Systems Security","url":"https://www.iec.ch"},{"name":"NIST SP 800-82 Rev.3 — Guide to Industrial Control System (ICS) Security","url":"https://csrc.nist.gov/publications/detail/sp/800-82/rev-3/final"},{"name":"ISA-95 / IEC 62264 — Enterprise-Control System Integration","url":"https://www.isa.org/standards-and-publications/isa-standards/isa-95-standard"},{"name":"NERC CIP — Critical Infrastructure Protection Standards","url":"https://www.nerc.com/pa/Stand/Pages/CIPStandards.aspx"},{"name":"SANS — SCADA Security and ICS Best Practices","url":"https://www.sans.org/white-papers/"},{"name":"NIST SP 800-82 Rev. 3 — OT configuration and operational considerations","url":"https://csrc.nist.gov/pubs/sp/800/82/r3/final"},{"name":"ISA — Automation standards and committees","url":"https://www.isa.org/standards-and-publications/isa-standards/isa-standards-committees"}],"related":[{"slug":"ot-identity-access-management-mfa","title":"OT Identity and Access Management: Accounts, Roles, and MFA","summary":"OT access works best with named identities, roles matched to jobs, and MFA placed at remote entry points rather than at every operator console.","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/ot-identity-access-management-mfa","markdown_url":"https://wiki.aspotomasyon.com/article/ot-identity-access-management-mfa.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/ot-identity-access-management-mfa","published":"2026-10-11T11:46:21+00:00","modified":"2026-10-11T11:46:21+00:00","reading_minutes":9,"word_count":1907,"image":"https://wiki.aspotomasyon.com/assets/social/ot-identity-access-management-mfa-2f4bbf8c3dfc.png"},{"slug":"mqtt-broker-deployment","title":"MQTT Broker Deployment and Hardening","summary":"MQTT is the de facto transport for industrial IoT telemetry: lightweight publish/subscribe over TCP, ideal for the many-to-many data flows of plant-to-cloud…","category":{"slug":"modern-connectivity","name":"Modern Connectivity"},"url":"https://wiki.aspotomasyon.com/article/mqtt-broker-deployment","markdown_url":"https://wiki.aspotomasyon.com/article/mqtt-broker-deployment.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/mqtt-broker-deployment","published":"2026-08-11T13:05:24+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":4,"word_count":871,"image":"https://wiki.aspotomasyon.com/assets/social/mqtt-broker-deployment-4fdd84765a13.png"},{"slug":"ot-security-architecture-defense-in-depth","title":"OT Security Architecture: Defense in Depth for Industrial Networks","summary":"Operational Technology (OT) environments — including industrial control systems (ICS), SCADA, DCS, and safety instrumented systems (SIS) — present unique…","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/ot-security-architecture-defense-in-depth","markdown_url":"https://wiki.aspotomasyon.com/article/ot-security-architecture-defense-in-depth.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/ot-security-architecture-defense-in-depth","published":"2026-05-13T12:07:53+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":10,"word_count":2092,"image":"https://wiki.aspotomasyon.com/assets/social/ot-security-architecture-defense-in-depth-427478438d17.png"},{"slug":"cloud-edge-ot-security","title":"Securing Cloud-Connected OT and Edge Deployments","summary":"Industry 4.0 architectures put edge devices and cloud services on the OT network's boundary: gateways that collect data and forward it to cloud platforms, edge…","category":{"slug":"industrial-cybersecurity","name":"Industrial Cybersecurity"},"url":"https://wiki.aspotomasyon.com/article/cloud-edge-ot-security","markdown_url":"https://wiki.aspotomasyon.com/article/cloud-edge-ot-security.md","api_url":"https://wiki.aspotomasyon.com/api/v1/articles/cloud-edge-ot-security","published":"2026-08-11T13:05:24+00:00","modified":"2026-09-13T11:07:23+00:00","reading_minutes":4,"word_count":874,"image":"https://wiki.aspotomasyon.com/assets/social/cloud-edge-ot-security-0cff76b6207f.png"}],"citation":"ASP OTOMASYON. SCADA System Security Hardening. Updated 2026-09-13. https://wiki.aspotomasyon.com/article/scada-system-security-hardening"}}